Sul server di casa girano servizi che uso ogni giorno. Se salta un backup o un container, me ne devo accorgere io; se lascio esposto un accesso, devo correggerlo io.Services I use every day run on my home server. If a backup or a container fails, I have to notice it; if I leave an access path exposed, I have to fix it.
Progetti / Infrastructure
srv1 Infrastructure
Un server in casa, su hardware consumer. Più servizi, rete controllata e backup con copia fuori sede.A server at home, on consumer hardware. Several services, a controlled network, and backups with offsite copies.
Il problemaThe problem
Cosa ho costruitoWhat I built
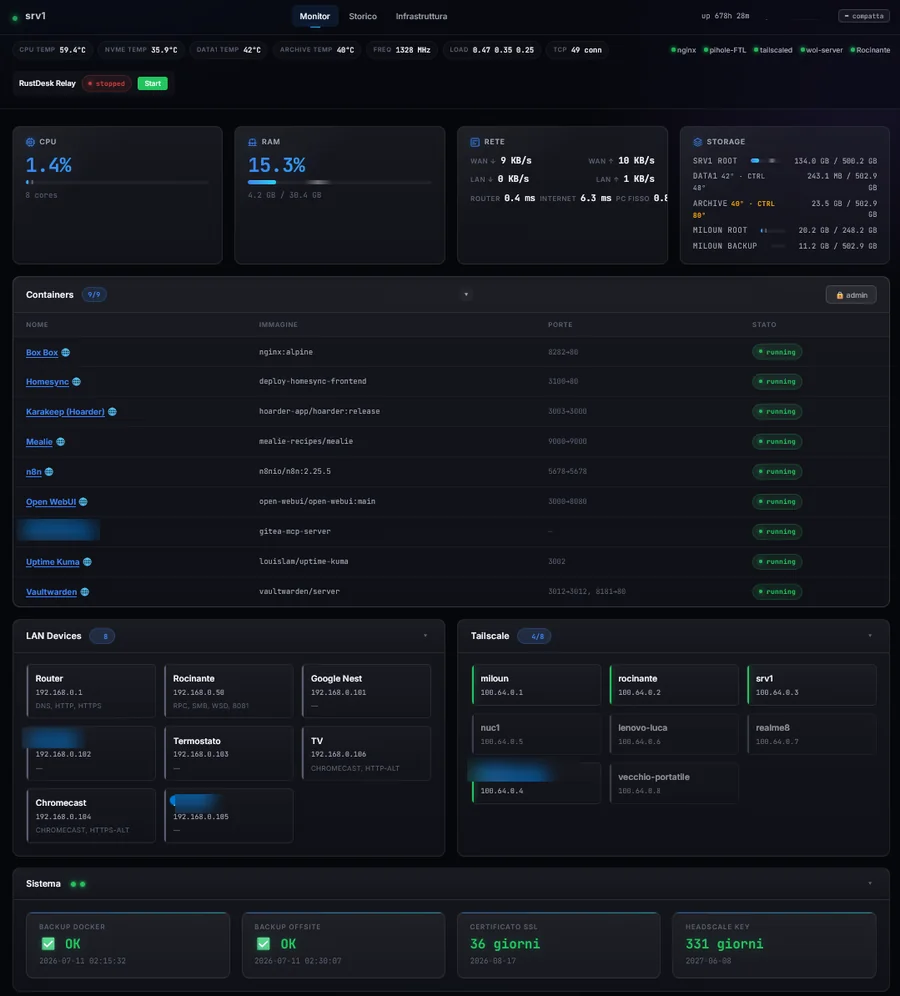
Ho separato i servizi pubblici dagli accessi amministrativi. Per entrare nella parte privata uso Tailscale con Headscale; il firewall è UFW. Tengo una copia dei backup fuori casa e controllo la destinazione. Dalla dashboard che ho scritto vedo risorse, container, eventi e stato dei backup. La mantengo perché è da lì che controllo il server.I separated public services from administrative access. I use Tailscale with Headscale for private access and UFW as the firewall. I keep an offsite backup copy and check the destination. The dashboard I wrote shows resources, containers, events and backup status. I maintain it because that's where I check the server.
Tech Stack
Linux Ubuntu
Docker
UFW
Tailscale
Headscale
rsync
Il codice e i dettagli del server restano privati. Posso spiegare come organizzo accessi, backup e controlli, senza pubblicare la configurazione.The code and server details stay private. I can explain how I handle access, backups and checks without publishing the configuration.
Chiedimi del progettoAsk me about the project